The surface
is not the
whole system.

Pentest, Red Team and vulnerability management run by people who actually attack — so you see what lies beneath the surface before an adversary does.

Methodology OWASP PTES NIST SP 800-115 MITRE ATT&CK
Test depth descending
  1. 0 mSurfaceExternal perimeter, DNS, exposed servicesRecon
  2. -3 mApplicationWeb, REST/GraphQL APIs and mobilePentest
  3. -6 mIdentityLeaked credentials, phishing, pretextingRed Team
  4. -9 mInternal networkActive Directory, lateral movementPentest
  5. -12 mThe basementWhere the real business impact livesTarget
surface ≠ system▼ we go deeper

Companies that have trusted Porão

From scoping to retest, no surprises.

A predictable engagement, with rules of engagement and test windows agreed in advance to keep impact on your operation to a minimum.

  1. 01

    Scoping

    We define targets, rules of engagement and test windows together with your team.

    Output: plan and timeline
  2. 02

    Reconnaissance

    We map the exposed surface: assets, technologies and leaked credentials.

    Output: attack map
  3. 03

    Exploitation

    Manual, controlled exploitation to prove real impact — not just list CVEs.

    Output: evidence
  4. 04

    Reporting

    Technical for those who fix, executive for those who decide. Always both.

    Output: 2 reports
  5. 05

    Retest

    We validate fixes for critical and high findings, included in scope.

    Output: fix confirmed

We attack so no one else can.

We are a company specialized in offensive security, focused on identifying, exploiting and mitigating vulnerabilities before they are exploited by malicious actors — with proven methodology, ethics and certified professionals.

Manual exploitation

Every finding is technically validated. No scanner dumps full of false positives.

Two audiences, two reports

Evidence, CVSS and reproduction steps for engineers; clear risk for leadership.

Retest included

The job ends only once fixes for critical and high findings are confirmed.

Business context

We prioritize by real impact on your operation, not just the vulnerability score.

Illustrative finding exampleTechnical report

PS-EX-007 High CVSS 8.1

IDOR exposes other customers' invoices

Asset
api.exemplo.com.br — /api/v2/invoices
Impact
Any authenticated user can read any customer's billing data by changing the ID.
Fix
Enforce resource ownership on the back end for every request.
# user A's session, user B's resource
GET /api/v2/invoices/10482 HTTP/2
Authorization: Bearer eyJhbGciOi…(user A)

HTTP/2 200 OK
{"owner":"cliente-b","cnpj":"**.***.***/0001-**",…}
AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:NRetest: fixed ✓
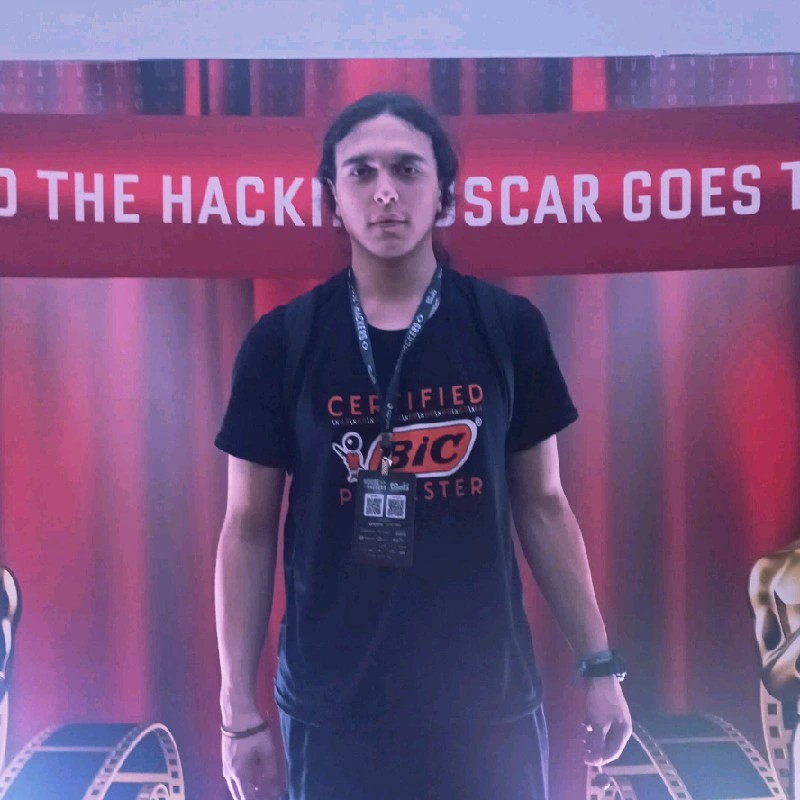
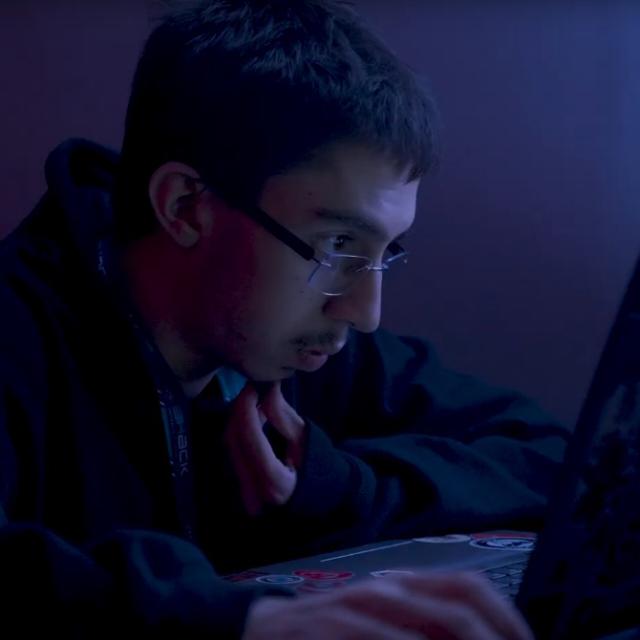
The people who run the tests.

Offensive operators with real-world experience — the same people you talk to during scoping sign the report.

Bruno Imperador

Bruno Imperador

Pentester & Red Team Operator

WebAPIMobileCloudInternal NetworkConsultantRisk-based priorityRemediationAdversary SimulationLateral MovementDefense EvasionC2 & Evasion
Diogo Scrivano

Diogo Scrivano

Pentester & Red Team Tool Developer

WebAPICloudInternal NetworkBusiness LogicConsultantMetrics & MTTRBlue TeamAdversary SimulationSocial EngineeringTooling DevelopmentDetection Validation

Team certifications

DCPT CEH CyberOps CTIP CPTP CCP CISO

Your company
could be next.

Attacks happen every day. The question isn't "if", but "when". Tell us your scenario and we'll reply within 1 business day.